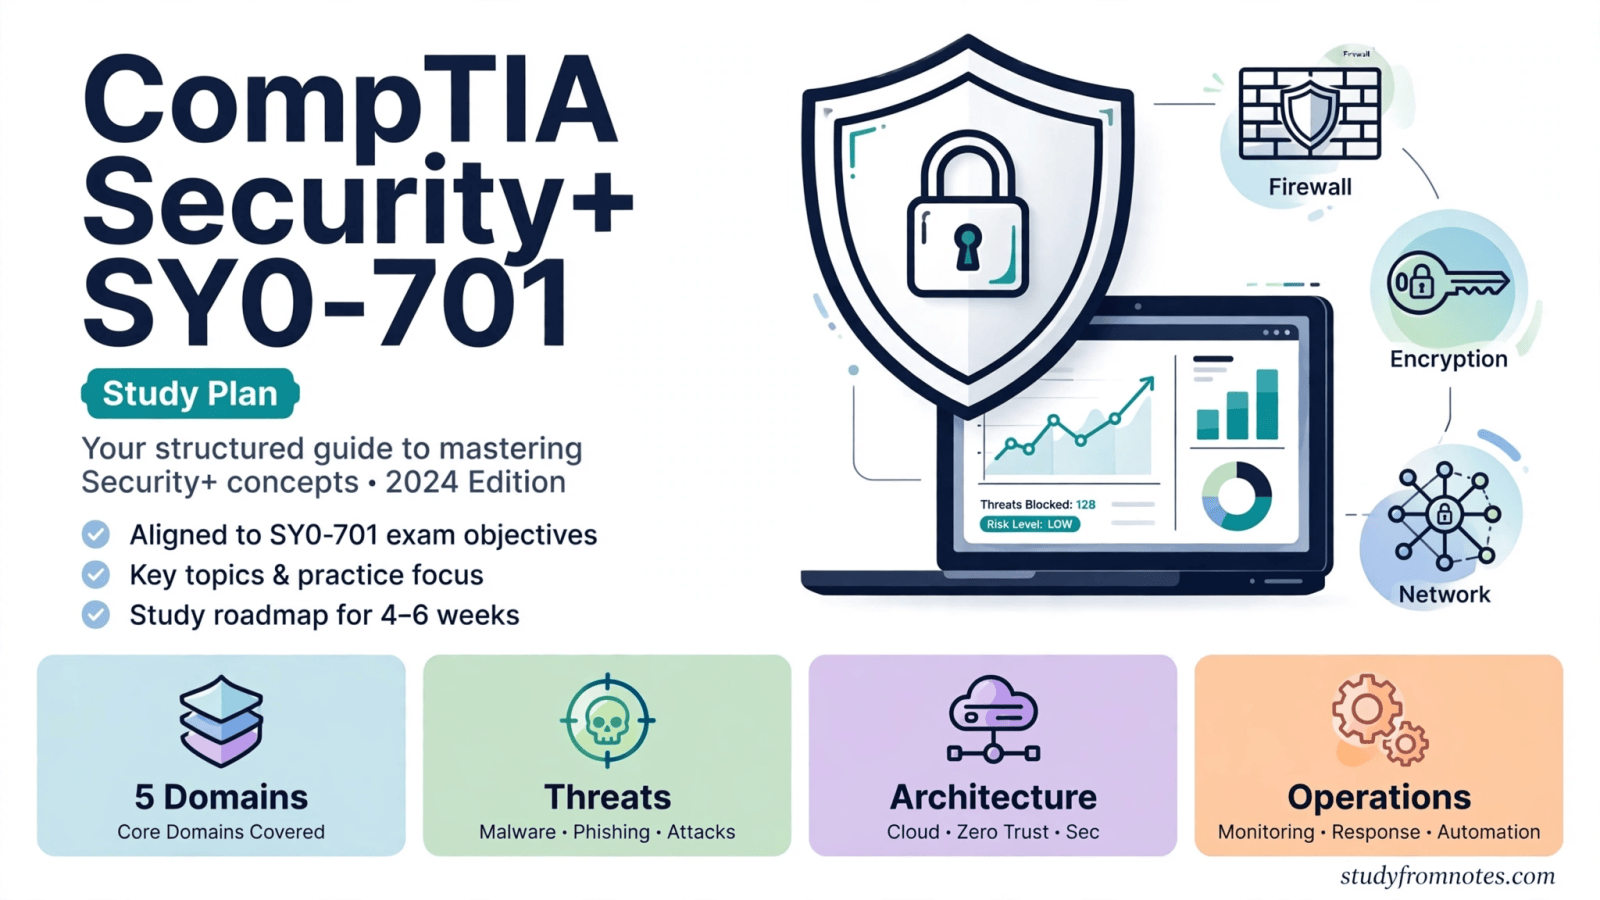
What Is the CompTIA Security+ SY0-701?
CompTIA Security+ SY0-701 is the current version of the leading entry-level cybersecurity certification. It validates baseline security skills across threats, architecture, operations, and governance, and it appears as a hard requirement in a large share of entry-level cybersecurity job postings.
If you want into cybersecurity without a degree in the field, Security+ is the most recognized first credential. This guide gives you the exam domains, a realistic study timeline, and a study method built for how this exam actually tests you.
Note: CompTIA expects to launch the successor exam, Security+ SY0-801, on or around November 17, 2026, and SY0-701 is scheduled to retire on June 11, 2027. Confirm the current version on CompTIA’s site before scheduling.
Planning your prep? Build a free day-by-day study timetable for this exam with our Study Timetable Generator.
Table of Contents
- Security+ SY0-701: The 5 Exam Domains
- How Long to Study
- Security+ SY0-701 Study Plan: Week by Week
- How Security+ Actually Tests You
- Performance-Based Questions: How to Handle Them
- Common Mistakes
- Exam-Day Strategy
- Frequently Asked Questions
Security+ SY0-701: The 5 Exam Domains
The SY0-701 exam has up to 90 questions (multiple-choice plus performance-based) in 90 minutes, with a passing score of 750 on a 100-900 scale. The five domains and their official weights:
| Domain | Weight | Focus |
|---|---|---|
| General Security Concepts | 12% | Security fundamentals, threat actors, attack vectors, security controls |
| Threats, Vulnerabilities, and Mitigations | 22% | Malware, social engineering, vulnerability scanning, penetration testing concepts |
| Security Architecture | 18% | Network security, cloud security, virtualization, secure protocols |
| Security Operations | 28% | Incident response, digital forensics basics, SIEM, automation |
| Security Program Management and Oversight | 20% | Governance, risk management, compliance, security policies |

How Long to Study
- With IT background: 6 to 8 weeks at 10 hours per week
- Without IT background: 10 to 12 weeks at 10 hours per week
The week-by-week plan below follows the 8-week track; without an IT background, stretch each phase to 10 to 12 weeks.
Security+ covers enormous breadth. The candidates who fail are usually those who studied deeply in one domain and skimmed the rest. Breadth first, then depth on weak areas.
Security+ SY0-701 Study Plan: Week by Week
Weeks 1-2: Security concepts and threats. Master the vocabulary: every attack type, every threat actor category, every control type. This is the foundation everything else builds on. Use flashcards for terms and spaced repetition to keep them.
Weeks 3-4: Architecture. Network security, cloud models, secure protocols. Draw every architecture concept by hand. If you cannot sketch how a DMZ or a VPN tunnel works, you do not know it yet.
Weeks 5-6: Operations. Incident response procedures, forensics basics, log analysis. This domain is the most scenario-heavy (28% weight), so practice with situational questions from day one.
Weeks 7-8: Governance and review. Risk management frameworks, compliance, policies. Then take full practice exams and drill your weakest domains.
Schedule it all with our free study timetable generator.
How Security+ Actually Tests You
Security+ is a scenario exam disguised as a vocabulary exam. Most questions present a situation (a log entry, a network diagram, an incident description) and ask what you would do. Memorizing definitions gets you perhaps half the marks. The other half comes from recognizing which concept applies to a messy real-world situation.
Study accordingly: for every concept you learn, invent a scenario where it applies. If you learn about spear phishing, write down what the phishing email looks like, who it targets, and what control stops it. Scenario-first studying mirrors the exam.
Performance-Based Questions: How to Handle Them
Security+ includes performance-based questions where you configure, match, or sequence items in a simulated environment. Performance-based questions are scored within the scaled-score model and can carry different weight than standard multiple-choice questions.
Strategy: do them first or last, but never in the middle. They consume disproportionate time and can rattle your confidence. Practice with any performance-based simulations your study materials include, and learn the interface patterns (drag-and-drop matching, firewall rule ordering) before exam day.
Common Mistakes
- Memorizing without scenarios. Definitions without application fail on this exam.
- Skipping governance. The management domain feels dry, but it is straightforward marks for candidates who study it.
- No timed practice. The exam is 90 questions in 90 minutes. Practice at that pace from week five onward.
- Ignoring acronyms. Security runs on acronyms. Keep a running glossary and review it weekly.
Exam-Day Strategy
On exam day, answer every multiple-choice question in a first pass without lingering: mark uncertain ones and move on. This guarantees you see all 90 questions and bank the marks you know. Return to marked questions with remaining time, and tackle performance-based questions in a dedicated block when your focus is fresh.
Read each scenario question twice before looking at the options. Security+ scenarios often contain a detail that eliminates two wrong answers immediately. The exam rewards careful reading as much as technical knowledge. If two answers both look correct, choose the one that addresses the root cause rather than the symptom: the exam consistently favors fundamental fixes over quick patches.
Frequently Asked Questions
Is Security+ enough to get a cybersecurity job?
It is the most requested entry-level credential in job postings, and it opens doors to analyst and specialist roles. Pair it with hands-on practice (home labs, CTF exercises) for the strongest applications.
Do I need Network+ first?
Not required, but networking knowledge helps significantly with the architecture domain. Candidates without it should add extra study time there.
How hard is the SY0-701?
It is challenging but fair. Candidates who study scenarios (not just terms) and take timed practice exams pass at high rates.
What comes after Security+?
Common next steps include CySA+ for analyst roles, PenTest+ for offensive security, or CISSP once you have the required experience.
Build Your Security+ Schedule
Map your domains across your available weeks with our study timetable generator, take notes with these 7 methods, and lock in terminology with spaced repetition.
Sources
Exam objectives and domain weights verified against CompTIA’s official Security+ page.

Lauren Brooks is a finance professional writing on professional exams, study strategies, and finance careers.
Leave a Reply